01 — Tool sprawl
Five tools, five consoles, blind spots between them.
Separate products for RMM, patching, remote access, assets and USB control multiply cost — and attackers live in the gaps.
Self-hosted security platform
One self-hosted security platform to manage every endpoint, lock down every device and grant zero-trust access to every app — on your own servers, inside your own borders.
Product UI shown with sample data
Built for
Why sovereign
That is why every AnvesionTech product is self-hosted by design: deployed on your servers, governed by your policies, inside your jurisdiction.
The problem
01 — Tool sprawl
Separate products for RMM, patching, remote access, assets and USB control multiply cost — and attackers live in the gaps.
02 — Cloud dependency
Cloud-only tools hold endpoint data, access decisions and logs outside your borders. Lock-in, outages and third-party access become your risk.
03 — VPN attack surface
Flat VPN access and exposed concentrators remain a top breach vector — a single compromised login enables lateral movement.
04 — Uninspected egress
GenAI prompts, webmail, USB, print and clipboard move regulated data every day — and access control alone never sees it.
The answer
Four products built to work together — deployed on your own servers, with every decision, log and byte of evidence kept inside your borders.
The platform
On-premise endpoint management, an immutable Linux OS, sovereign zero trust access and self-hosted virtual desktops — designed to run together on infrastructure you control.
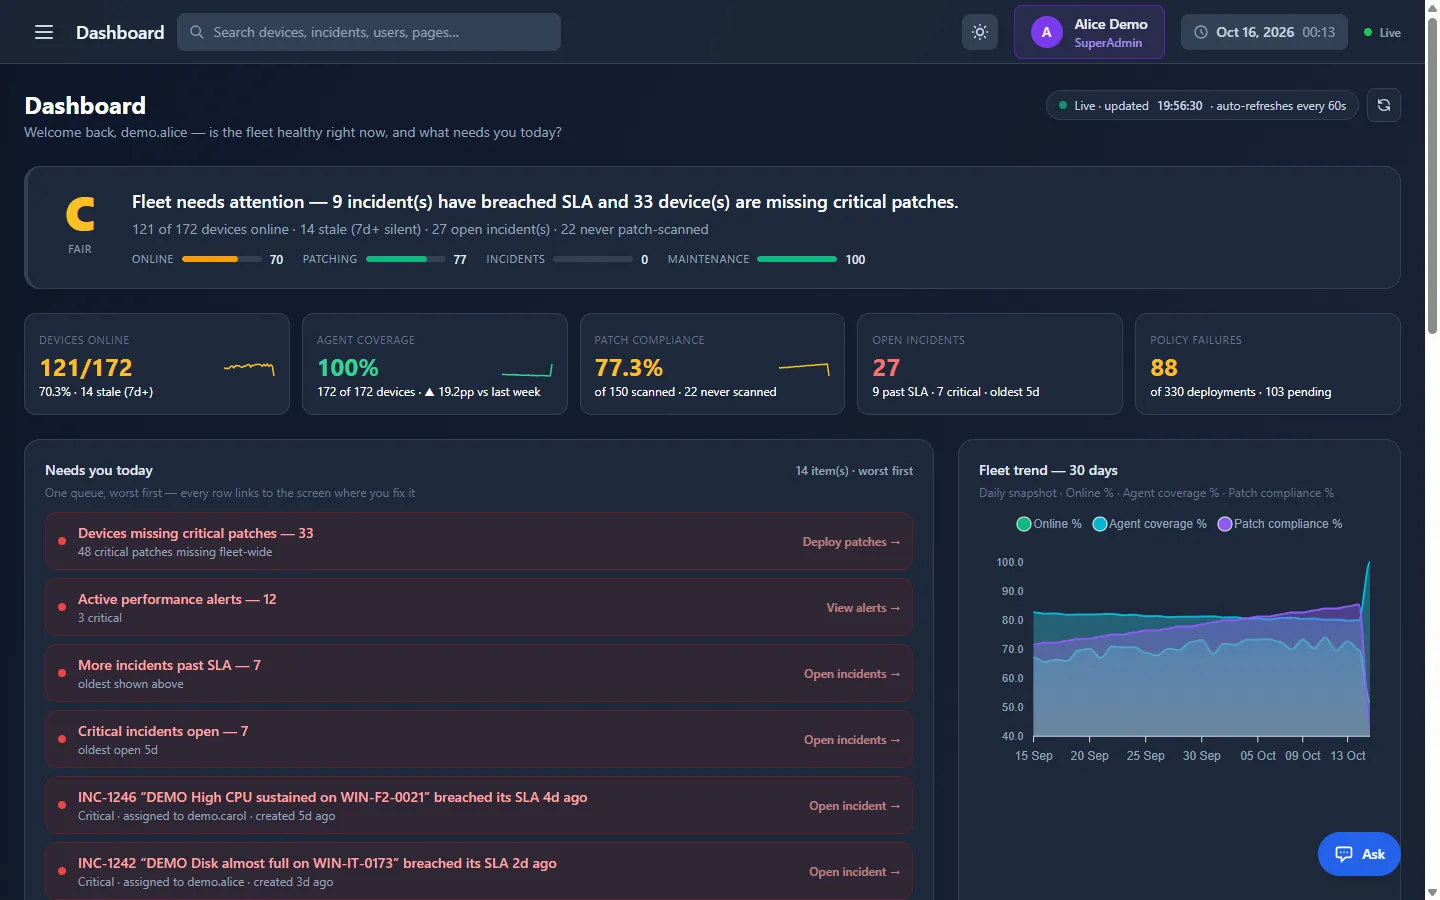
01Endpoint management & RMM · v7.0
Discover, secure, patch and support every Windows and Linux endpoint from one self-hosted console.
02Immutable Linux OS · x86 & ARM
A signed, read-only operating system that can't be tampered with or bricked by an update — managed at fleet scale.
Boot · verifySecureOS
03Zero trust access · PAM · DLP
Retire the VPN. A self-hosted VPN replacement that makes private apps invisible and inspects every channel data could leave by.
04Virtual desktops · Windows & Linux
Self-hosted virtual desktops and published apps, delivered to a browser tab or a SecureOS thin client.
VDI host · your data centreSelf-hosted
Windows desktopsLinux desktops
How it fits together
Access layer
Decides who reaches which app, from which verified device — and inspects what leaves.
Delivery layer
Windows and Linux desktops and published apps, served from your data centre.
Management layer
Every endpoint seen, patched, assessed and controlled from one console.
Endpoint OS
Immutable and unbrickable. Managed by DeviceManager, and a ready VDI thin client.
Foundation
On-prem, private cloud, hybrid or air-gapped — the data never leaves it.
New in DeviceManager 7.0
Four new modules take DeviceManager beyond endpoint management — all on the same self-hosted server.
Vulnerability assessment (VAPT)
No extra scanner, no network scanning: agent inventory is matched against Microsoft, Linux, NVD, CISA and FIRST threat data.
Agent-based vulnerability assessmentNetwork monitoring (SNMP)
Routers, switches, printers and UPS units over SNMP — topology map, configuration backup and traps. No licence seat.
SNMP network monitoringAI Assistant
Read-only lookups that run with your permissions. A local model keeps every question inside your network.
DeviceManager AI AssistantWrite Filter kiosk lockdown
Windows IoT Enterprise and LTSC devices held in a defined Unified Write Filter state — reboots handled, never left unprotected.
Write Filter policies in DeviceManagerPrinciples
Runs on your servers. Endpoint, access and audit data stay inside your perimeter.
RBAC, MFA, AD/LDAP, signed commands and a complete audit trail — built in.
Watchdog recovery, A/B rollback and self-healing connectors keep endpoints working.
Maker-checker, tamper-evident audit and India-resident retention, ready for review.
Compliance alignment
Audit-ready technical controls that support RBI, SEBI, CERT-In, DPDP, PCI DSS, HIPAA, NIST and CIS requirements. Data sovereignty in India comes by architecture: the evidence stays on your servers.
Hash-chained logs make any alteration detectable, with integrity verified on demand.
Privileged operations need a second approver — the maker can never be the checker.
180-day encrypted audit-log retention, inside your jurisdiction.
Lawful-basis evidence and data-principal rights for DPDP, actioned in your own console.
Audit-ready technical controls that support compliance. Formal certification is a separate, third-party engagement.
Deploy your way · Who it's for
No vendor cloud required
Beyond products
VoIP communication platform
Asterisk with our own ARI control application and 2+2 server redundancy — also deployed for call centres, BPOs, manufacturing and edge sites.
Railway VoIP platformCar shed management
A railway car shed management system that flags maintenance needs before they become failures.
Car shed managementAlso built to order
Let's talk
Get a tailored demo, a pilot in your own environment, and a clear deployment and licensing plan for DeviceManager, SecureOS, Sovereign ZTNA, VDI or a custom solution.